BlueArc Cert

Audit readiness workspace

Walk into your audit with the proof already organised.

BlueArc Cert gets your business ready for ISO 27001, SOC 2, GDPR, NIST CSF and the Essential Eight in one place. Every control, policy and piece of evidence has an owner, a date and a record.

AUD 1,999per organisation per year, including GST
14 daysfree to try every feature
Sydneyyour data is hosted in Australia

ISO 27001  |  SOC 2  |  GDPR  |  NIST CSF  |  Essential Eight

75% ready  85 of 113 controls covered
bluearccert.com
BlueArc Cert Overview screen showing a 75 percent readiness score, progress bars for each clause and a readiness trend over four months

Screens show a sample organisation, Tallowood Analytics.

Why accreditation is hard

Getting certified is mostly an organisation problem.

Many of the controls may already be in place. The proof sits across inboxes, shared drives and spreadsheets with no clear owner.

Too many moving parts

ISO/IEC 27001 alone has 118 controls and clauses, each needing a policy, an owner and current evidence.

Evidence goes stale

A quarterly access review that was current in March is out of date by July, and nobody notices until the auditor asks.

No single picture

Leaders cannot see how close they are, so the audit date drives a last minute scramble.

Auditors need a clean record

They want to see who approved what, when, and that files were not changed after review.

Consultants are expensive

Paying someone to chase spreadsheets adds cost without adding security.

One effort, many standards

Five standards. One body of work.

Map a policy once and reuse it across ISO 27001, SOC 2, GDPR, NIST CSF and the Essential Eight. Work done for one counts toward the others where controls overlap.

Control wording in BlueArc Cert is preparation guidance. Confirm wording and scope against the official standard.
StandardVersionControls and requirements
ISO/IEC 270012022118
NIST Cybersecurity Framework2.0106
SOC 2 Trust Services Criteria201738
GDPRRegulation (EU) 2016/67938
Essential EightNovember 202324

How it works

Seven steps from first sign in to audit ready.

BlueArc Cert covers everything up to the audit itself. Your accredited certification body then reviews and certifies.

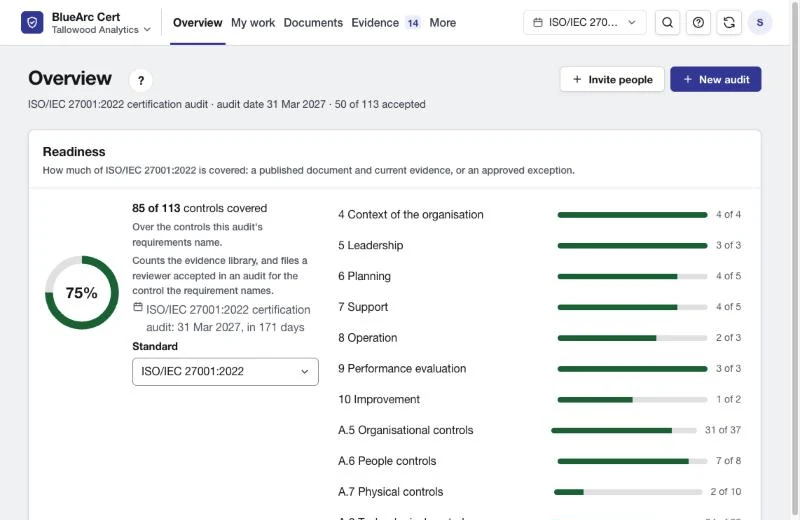
Step 1   Know where you stand

See how ready you are, every day.

The Overview answers the question every leader asks: how ready are we?

  • A live readiness score for each standard and each clause
  • A month by month trend, so progress is visible
  • Next best actions and what is overdue, without a status meeting

Business benefit. Leaders see progress in seconds and the team knows exactly what to do next.

bluearccert.com
Overview screen with readiness score and clause progress bars

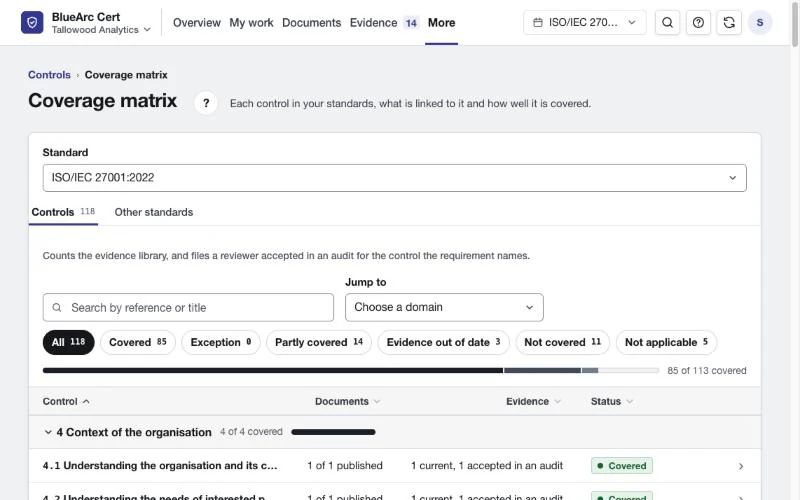
Step 2   Set your scope

Decide what applies. See every gap.

Decide which controls apply to your business and why. Each decision is recorded with its reason and flows into your Statement of Applicability, the document auditors read first.

  • Applicability decisions with reasons
  • A coverage matrix, clause by clause, with clear status chips
  • An owner and a due date on every control

Business benefit. No control is forgotten, every gap has an owner and your scope decisions are documented the way an auditor expects.

bluearccert.com
Coverage matrix listing each control with documents, evidence and status

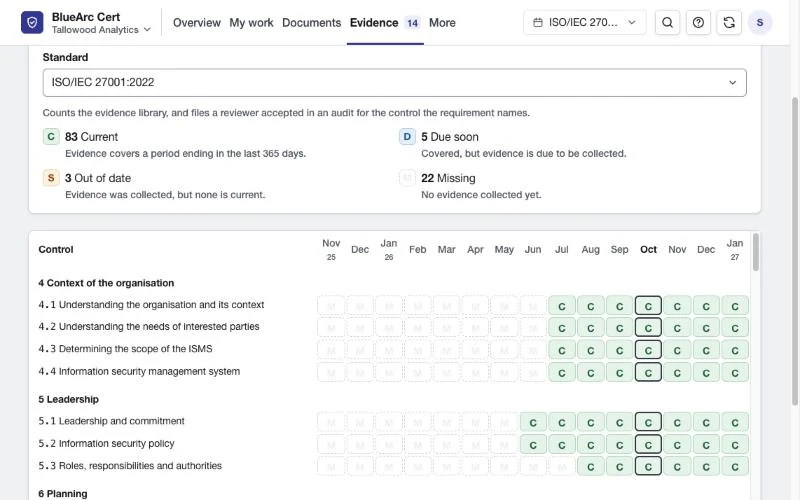
Step 3   Collect evidence

Evidence that stays current.

The Evidence library holds the reports, minutes, training records and screenshots that prove each control works.

  • An owner, a due date and a frequency for every item
  • Saved versions that can never be overwritten, each independently reviewed
  • A freshness calendar that shows what is Current, Due soon, Out of date or Missing

Business benefit. No more hunting for files the week before the audit, and no surprises when the auditor checks dates.

bluearccert.com
Evidence freshness calendar showing each control by month

Step 4   Write your policies

Policies done properly, and fast.

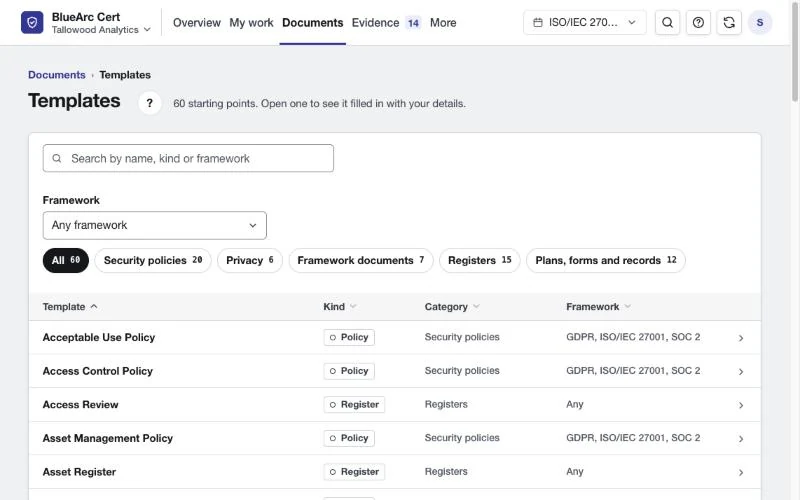
You do not start from a blank page. Open a template and your company details are filled in for you.

  • 60 templates across security policies, privacy, framework documents, registers, plans and forms
  • Edit in the app, then download as a Word file or print to PDF
  • Signed approvals with the approver's name, role and date, and staff acknowledgements

Business benefit. Policies are written faster, approved properly and reused across standards, which cuts effort and consultant time.

bluearccert.com
Template library filtered by framework and category

Step 5   Manage risk

Risks, suppliers and registers together.

Registers hold the records an auditor asks for, in the same place as your controls and evidence.

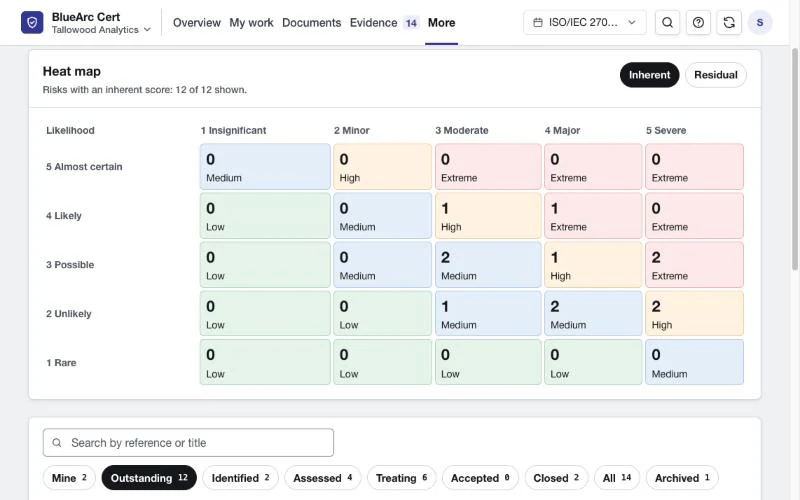
  • A risk register with an inherent and residual heat map
  • A supplier register with criticality, sub processors and review dates, exportable to CSV
  • 15 registers in total, including incidents, changes, assets and access reviews

Business benefit. Risk and supplier management, which every standard asks for, sits alongside your controls instead of in separate spreadsheets.

bluearccert.com
Risk heat map showing likelihood against impact

Step 6   Run the day to day work

Everyone knows what to do next.

Accreditation becomes part of normal work, spread across the team, rather than one person's side project.

  • A task board with To do, In progress, In review and Done
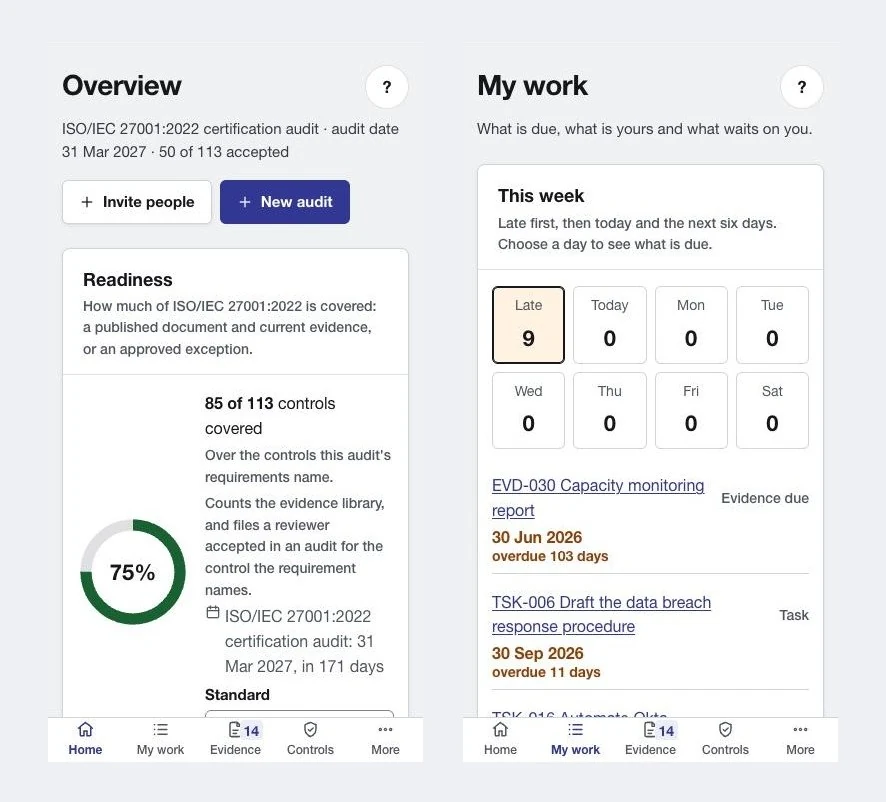
  • My work: what is late, what is due today and what is due this week
  • Works on a phone, with a bottom menu for Home, My work, Evidence, Controls and More

Business benefit. Owners can check and act on the go, and overdue work is flagged before it becomes a delay.

BlueArc Cert Overview and My work screens on a phone

Step 7   Be audit ready

Hand your auditor a clean record.

Freeze the audit when its evidence is reviewed. The audit pack is a fixed record of the audit and every accepted file, with each file's hash so anyone can prove nothing changed afterwards.

  • Read only auditor access, granted per audit, with internal notes never shown
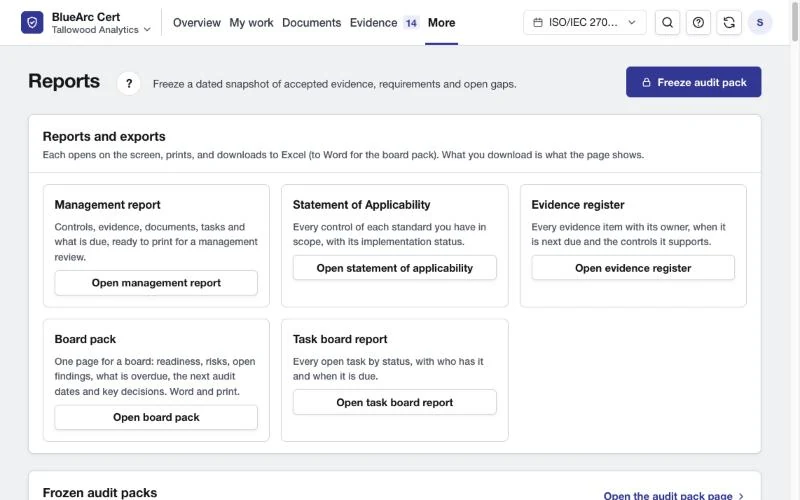
  • Statement of Applicability, management report, evidence register, board pack and task board report
  • Download to Excel, with the board pack also in Word, or print

Business benefit. You hand the auditor a complete, tamper evident record instead of a folder of attachments, so the audit runs on facts rather than follow up requests.

bluearccert.com
Reports page listing the management report, Statement of Applicability, evidence register, board pack and task board report

Overview

Two minutes. The whole product.

See the seven steps on screen, from first sign in to a frozen audit pack.

Security and trust

Built to the standards it helps you meet.

A compliance tool holds your most sensitive records, so BlueArc Cert is built with the same care it asks of you.

Two factor sign in for everyone

Every member needs an authenticator app, and each browser tab signs in on its own.

Stored in Australia

Your data is hosted in Sydney.

Your data stays yours

Each organisation's records are separated in the database itself. In testing, a signed in user from another organisation saw zero rows across 100 tables.

Evidence cannot be altered

Uploaded files cannot be overwritten. A change is a new version, and every version needs its own independent review.

Tamper evident audit packs

A frozen audit pack records each accepted file's hash.

Suspicious files are stopped

Uploads that are not what they claim to be are quarantined and removed automatically.

Least privilege for auditors

Auditor access is read only and granted per audit. Internal notes are never shown to them.

A full audit log

Every action records who did what and when. The site runs on HTTPS only with HSTS and a strict content security policy.

Ownermanages ownership of the organisationAdminmanages audits and assignmentsContributorsubmits assigned work and evidenceReviewerassesses evidence and records the decisionAuditorread only access to the audits they are granted

Pricing

One plan. Every feature. Priced per organisation.

Invite your whole team and assign owners from day one. The price is per organisation, so a bigger team does not cost more.

Pick a standard, apply templates and watch your readiness score rise.

BlueArc Cert

$1,999AUD per year

Per organisation, including GST. Start with a 14 day free trial, no card needed.

  • ISO/IEC 27001, SOC 2, GDPR, NIST CSF and the Essential Eight
  • 60 policy and document templates with signed approvals
  • Evidence library with locked versions and a freshness calendar
  • Risk register, supplier register and 15 registers in total
  • Task board, My work and phone access
  • Auditor access, frozen audit packs and reports
  • Invite your team from day one, at one price per organisation
Start your 14 day free trial

Everything works during the trial except Export everything. Add payment when you are ready, and Stripe takes it securely. The plan renews yearly and you can cancel any time from Settings.

Questions

A few good questions.

Rather talk it through first? Email support@bluearccert.com.

Does BlueArc Cert certify my business?

Your accredited certification body performs the audit and issues the certificate. BlueArc Cert gets you ready for it and gives the auditor a clear, trustworthy record.

Which standards are covered?

ISO/IEC 27001:2022 (118 controls and clauses), NIST Cybersecurity Framework 2.0 (106), SOC 2 Trust Services Criteria 2017 (38), GDPR (38) and the Essential Eight, November 2023 (24). Work done for one counts toward the others where controls overlap.

What does it cost?

AUD 1,999 per organisation per year, including GST. There is one plan with every feature, and the price is per organisation, not per person.

What happens in the 14 day trial?

Every new organisation gets 14 days free with no card. Everything works except Export everything, which unlocks when you subscribe. Invite your team, assign owners, pick a standard, apply templates and watch your readiness score rise.

What happens when the trial ends?

An owner or administrator subscribes from inside the app, and Stripe takes payment securely. If the trial ends without a subscription, the organisation becomes read only. Nothing is deleted.

Can I cancel?

Yes, at any time from Manage billing in Settings. Cancelling stops the next yearly renewal, and access continues until the end of the year you have paid for.

Where is my data kept, and who can see it?

Your data is hosted in Sydney. Each organisation's records are separated in the database itself, and every member signs in with two factor authentication. Auditors receive read only access to the audits you grant them.

Can my auditor use it?

Yes. Auditors get their own read only access, granted per audit, so they see exactly what they need. Their questions arrive on the control itself, and your internal notes are never shown to them.

Can I use it on my phone?

Yes. BlueArc Cert works on a phone, with a bottom menu for Home, My work, Evidence, Controls and More, so owners can check and act on the go.

Can I edit the policy templates?

Yes. Open a template and your company details are filled in. Edit it in the app, save each change as a new revision, and download it as a Word file or print it to PDF. Approved versions stay as they were approved.

Is the control wording official?

The control wording in BlueArc Cert is preparation guidance. Confirm wording and scope against the official standard.
Start your 14 day free trial.

No card needed. Pick a standard, apply the templates and see your readiness score from day one.